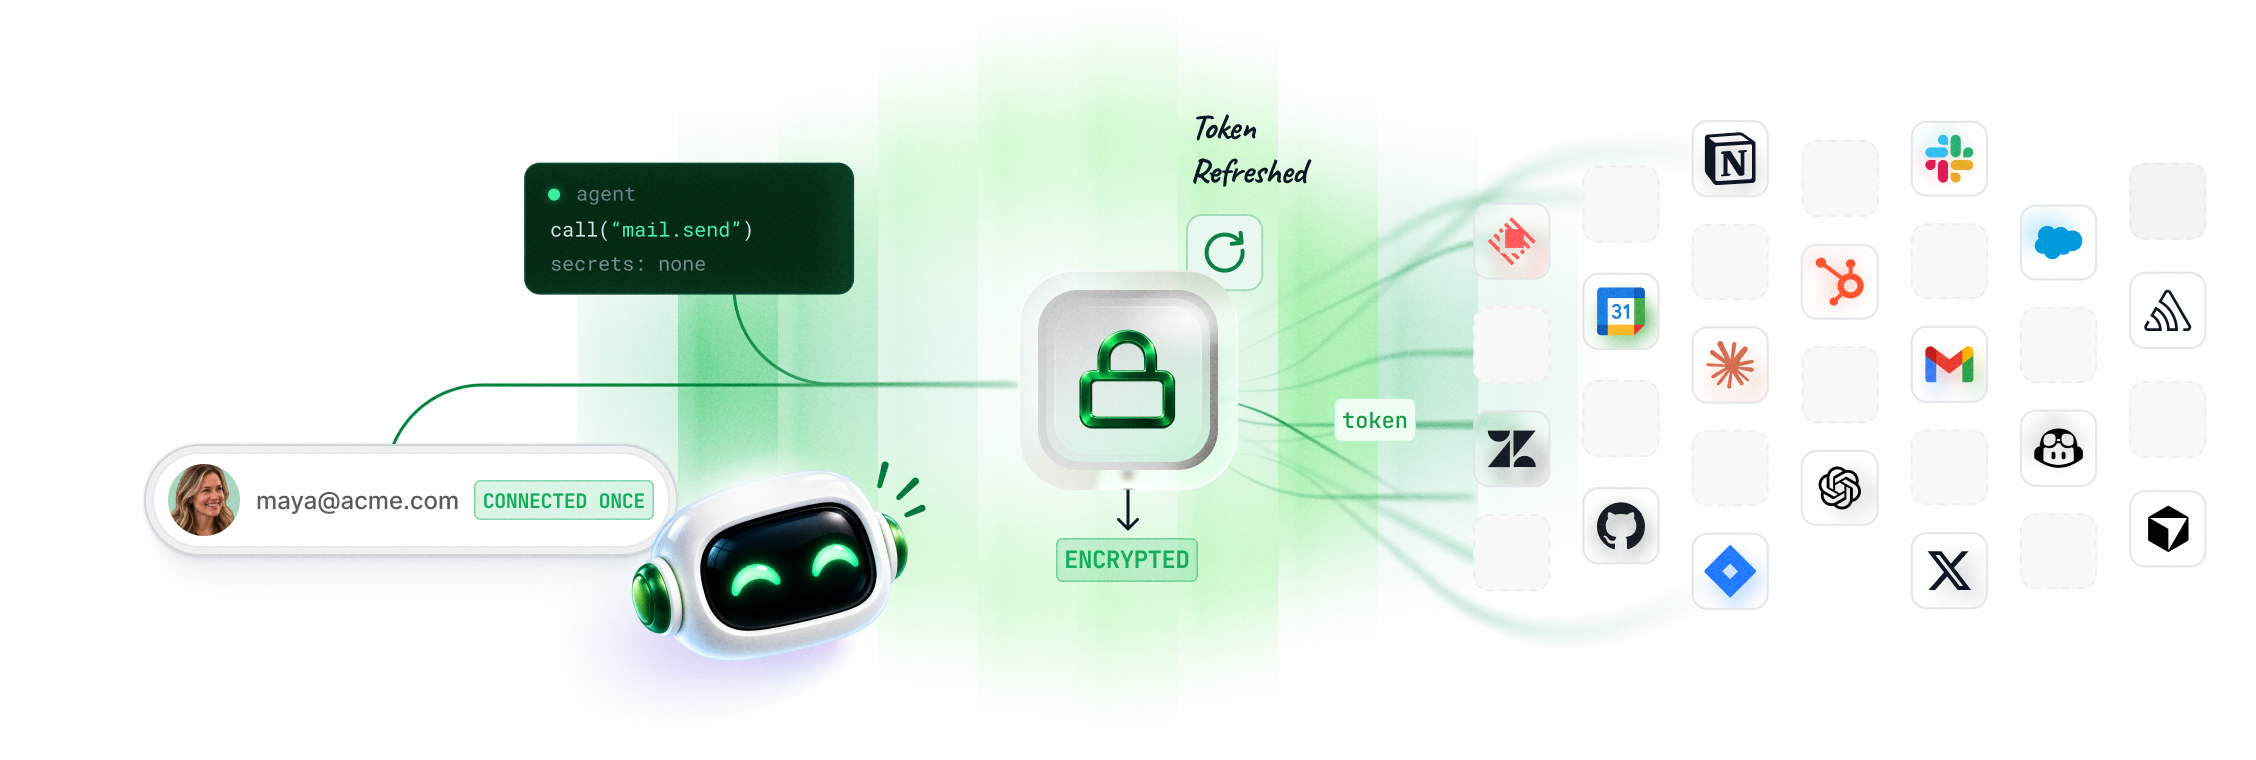
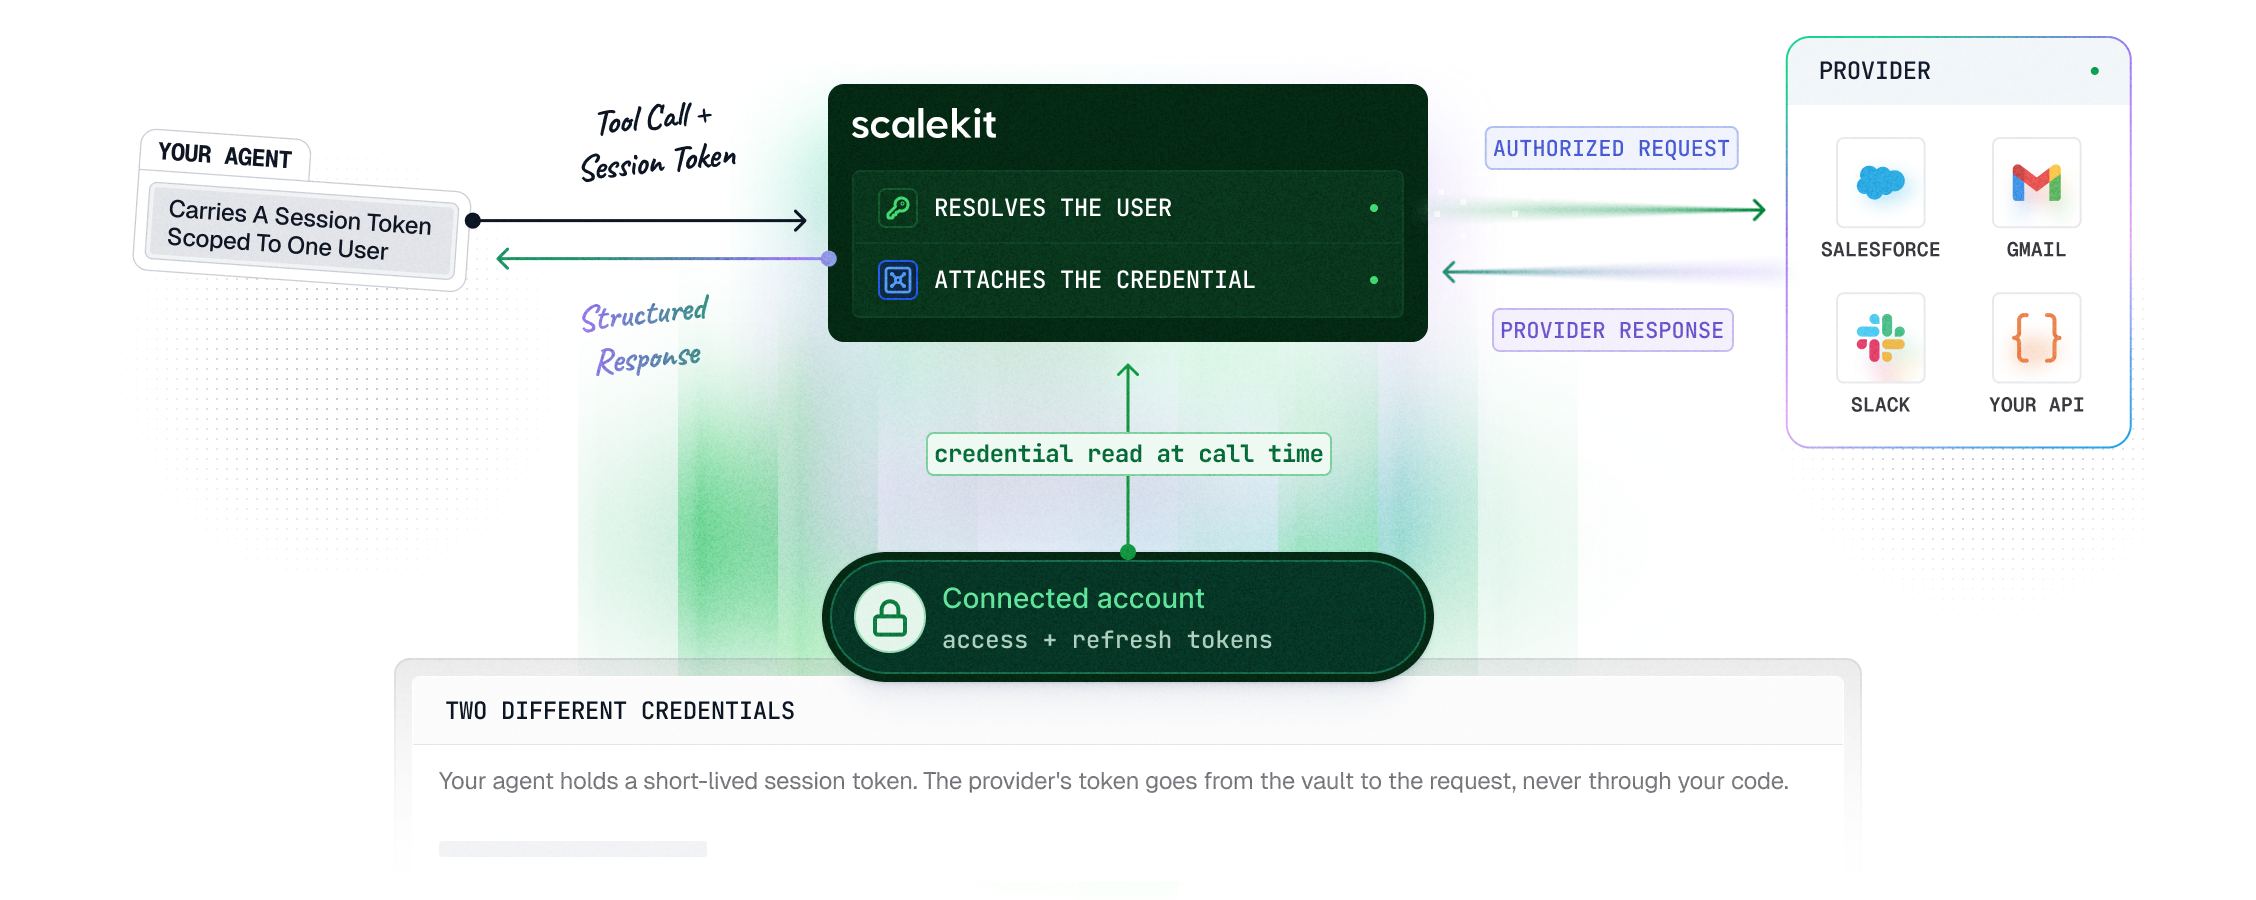
Your agent acts as the user. Not as a service account.
A shared service account means every one of your customers is trusting a single set of credentials with access to all of them. Connected accounts invert that: each user authorizes their own, and a run can only ever reach the accounts of the person it was minted for.
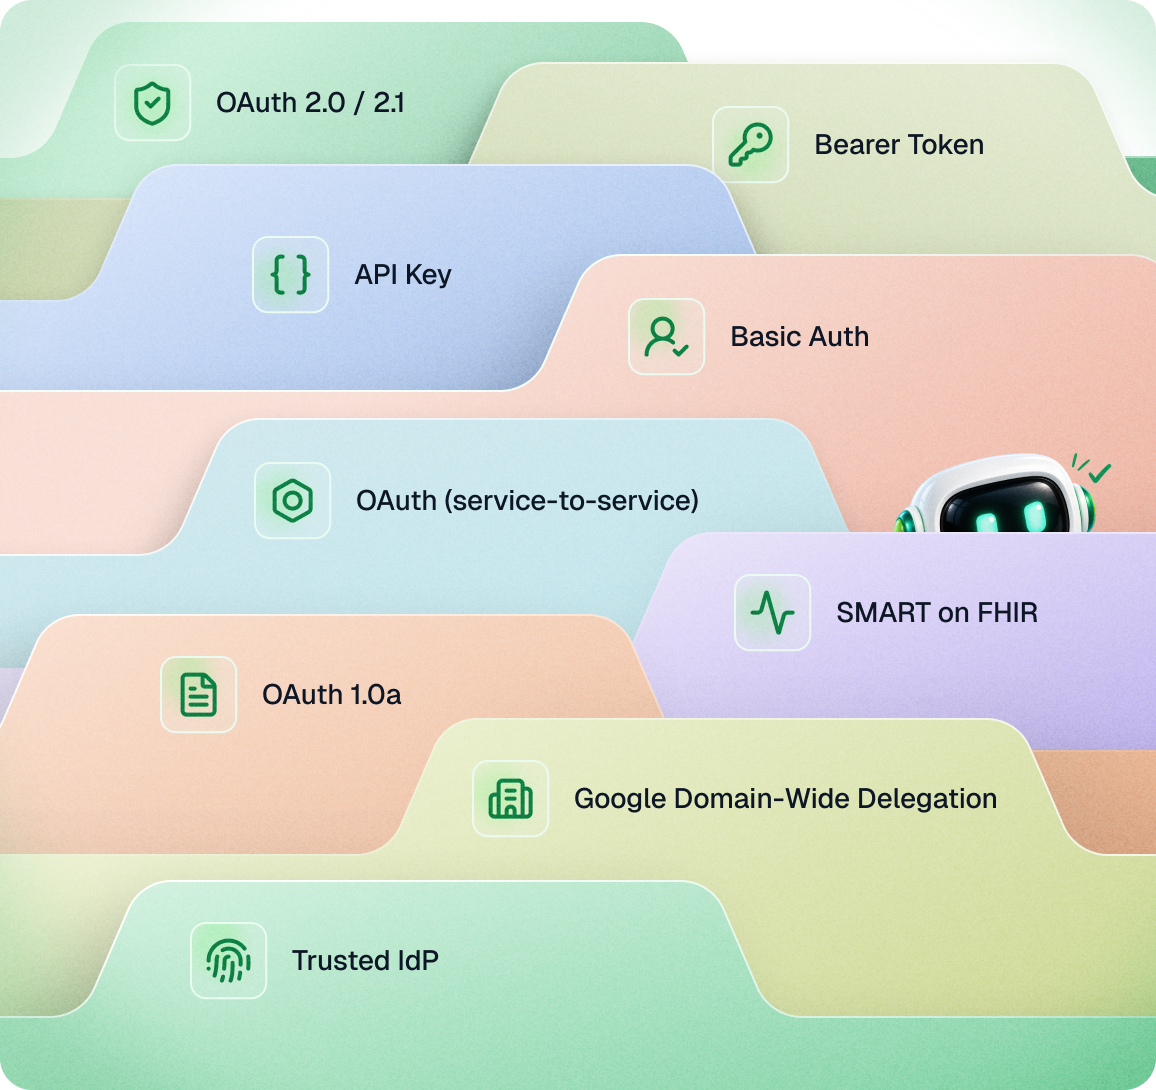
Every auth model in the catalog. One code path on your side.
OAuth, API keys, SMART on FHIR or anything else: your call looks the same. Everything after the grant is ours.
Stored and injected for you. Encrypted per tenant, never in your code or prompts.
Refreshed before they lapse. Long runs don't fail on an expired token.
Rotated without an outage. Keys roll on schedule,no deploy needed.
Revoked cleanly. You get a re-auth link, not a 401.
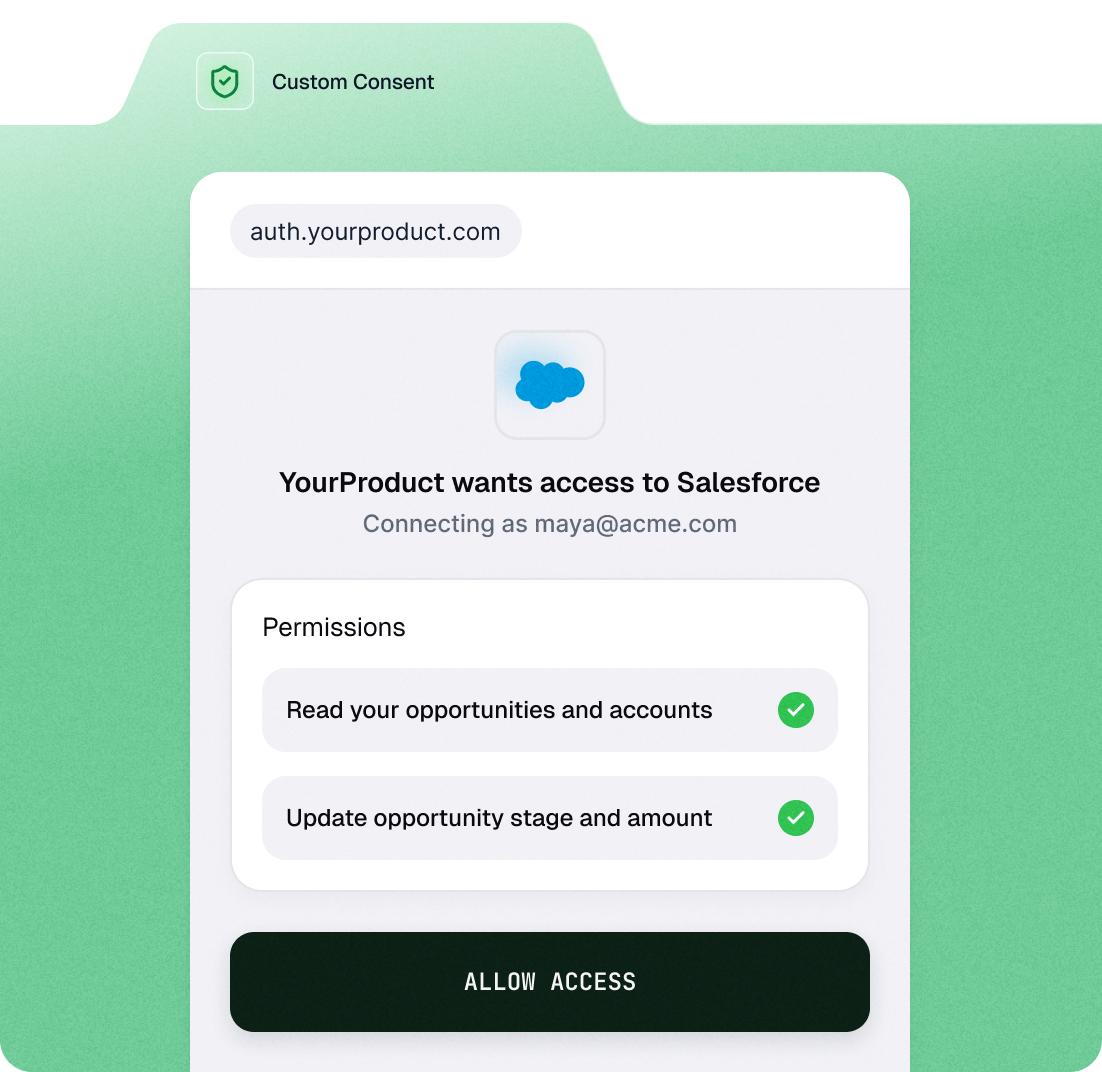
The consent screen is yours. Not ours.
Your users are authorizing your product, so they must see your name and your domain, not an infra providers.
Your brand, your domain. No third party shows up in the flow.
Your own OAuth app. Providers show your app's name, not ours.
Only what the role needs. No write scopes an agent never uses.
Re-consent when it lapses. An auth link you show in your own UI.
Hold your own keys. We never see a plaintext credential.
Bring your own key from your KMS. Every token is encrypted with it, and you can revoke it anytime.
You own the key
Created in your KMS, under your rotation policy.
You own the key
We can encrypt and decrypt. The key never leaves your KMS.
You can revoke
Pull the grant and every stored token is unreadable, including to us.
Nothing changes upstream
Your agents and tool calls work exactly the same.
Stop owning the auth layer. Start on the agent.
Free to start, no credit card. Connect one account and watch a token neverreach your code.