Start for free
PRODUCTS
Agentkit
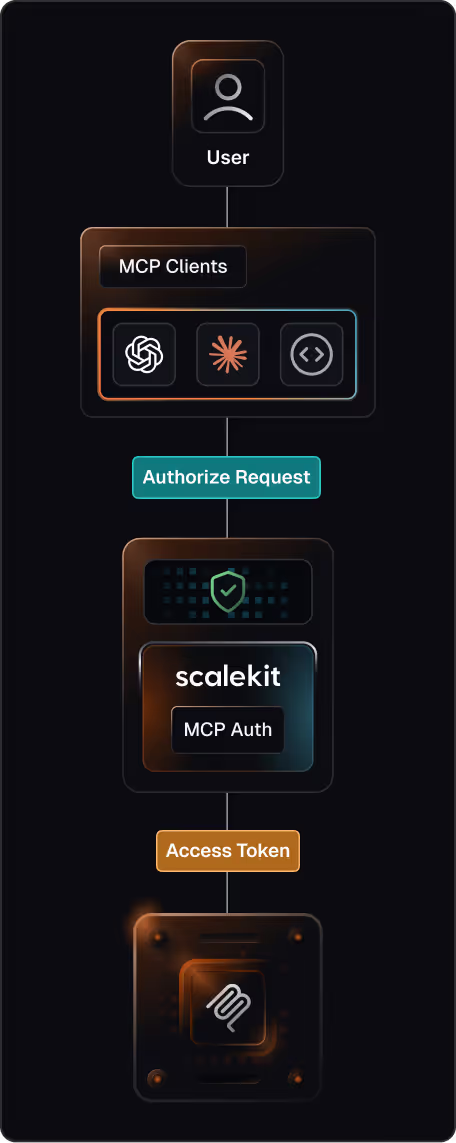
MCP Gateway for agents
Connectors & Tools
500+ apps, plus your own
Auth & credentials
Per-user tokens, handled
Virtual MCP servers
Scope tools by agent role
Triggers
Run agents on events
Logs
Every call, attributed
Enterprise
BYOK, VPC, and compliance
Also from scalekit
MCP Auth
OAuth 2.1 for MCP servers
Auth for saas
SSO, SCIM & RBAC for B2B
Agent gateway
Control team agent access
connector catalog
customers
PRICING
resources
COMPARE
Pick the right agent integrations platform
VS COMPOSIO
See how security stacks up
VS NANGO
See which is built for agents
Guides & research
Interactive Guide
Build or buy agent integrations?
Score 8 questions, get a build-or-buy decision framework
new report
Agents on the clock
See what a month of tool calls reveals
DOCS
Talk to US
Start for free
User and org management,
built for B2B apps
A multi-tenant identity model purpose-built for users, roles, and policies scoped to each organization
Start for free
View docs
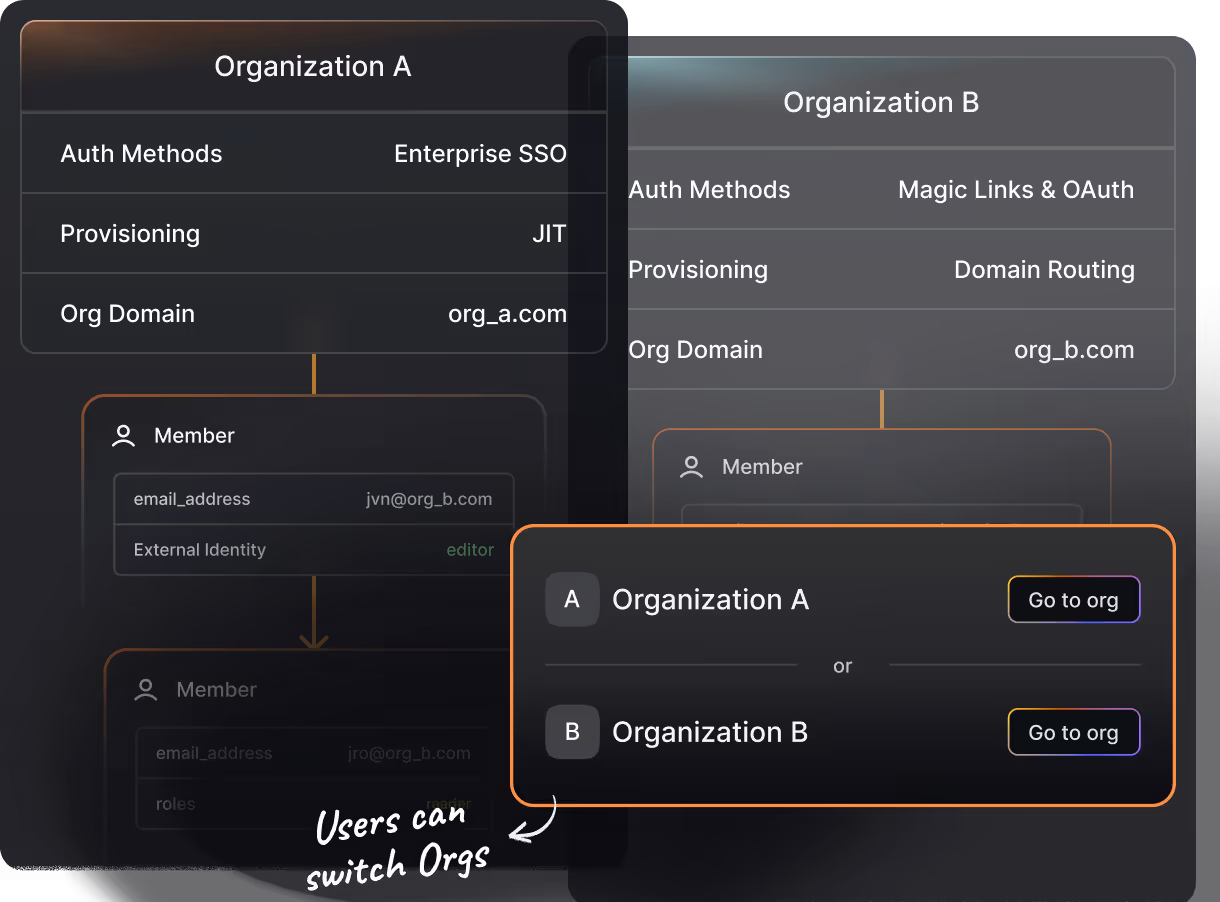
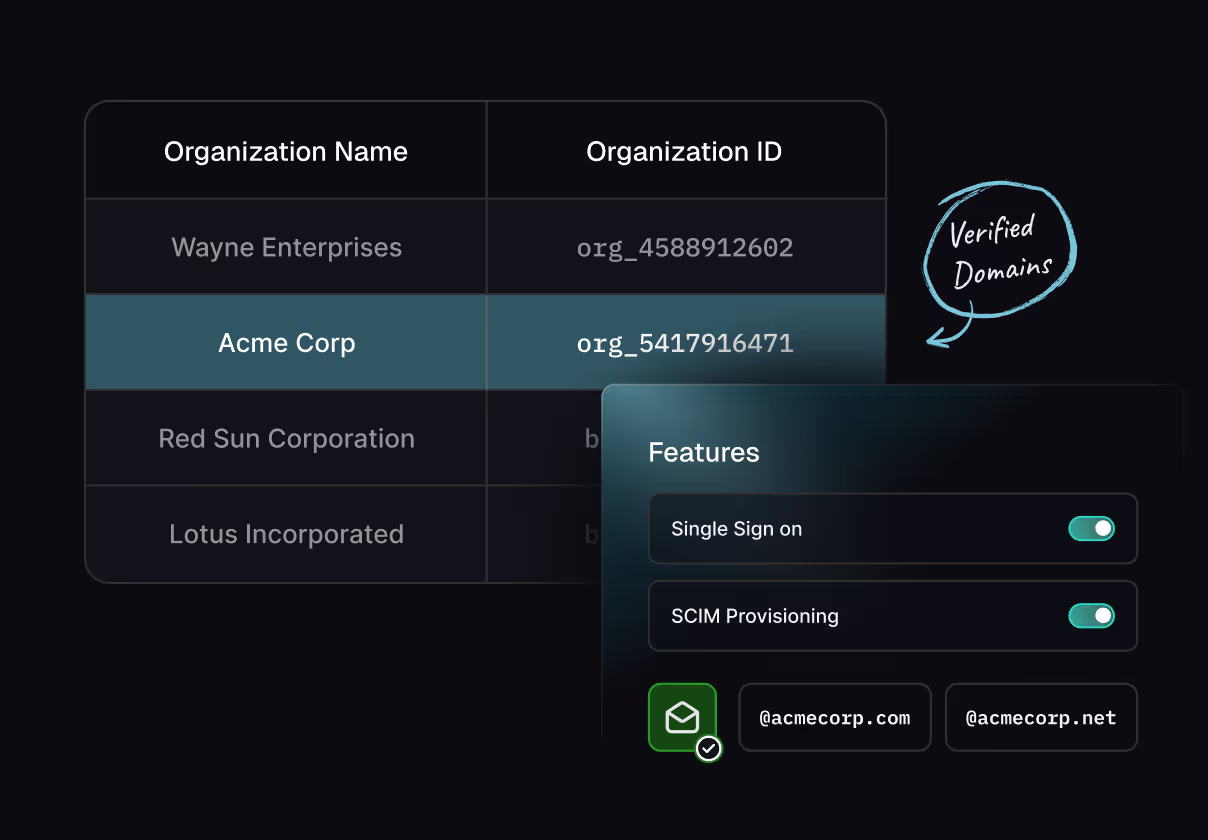
Organizations as a first-class identity primitive
Users, roles, and access are natively modeled with organizations as the primary context
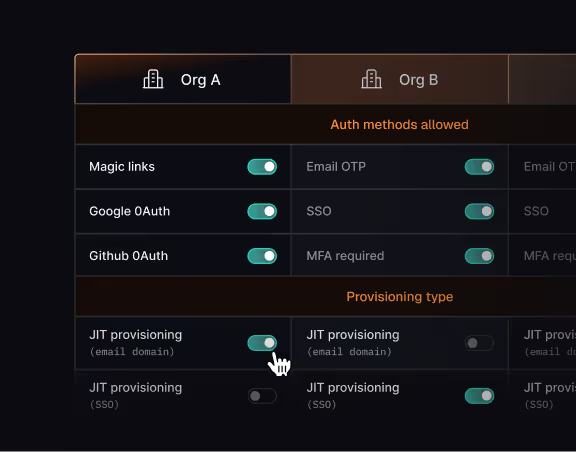
Multi-tenant by default
Each organization is isolated by design, with its own users and auth policies, no custom tenancy code required
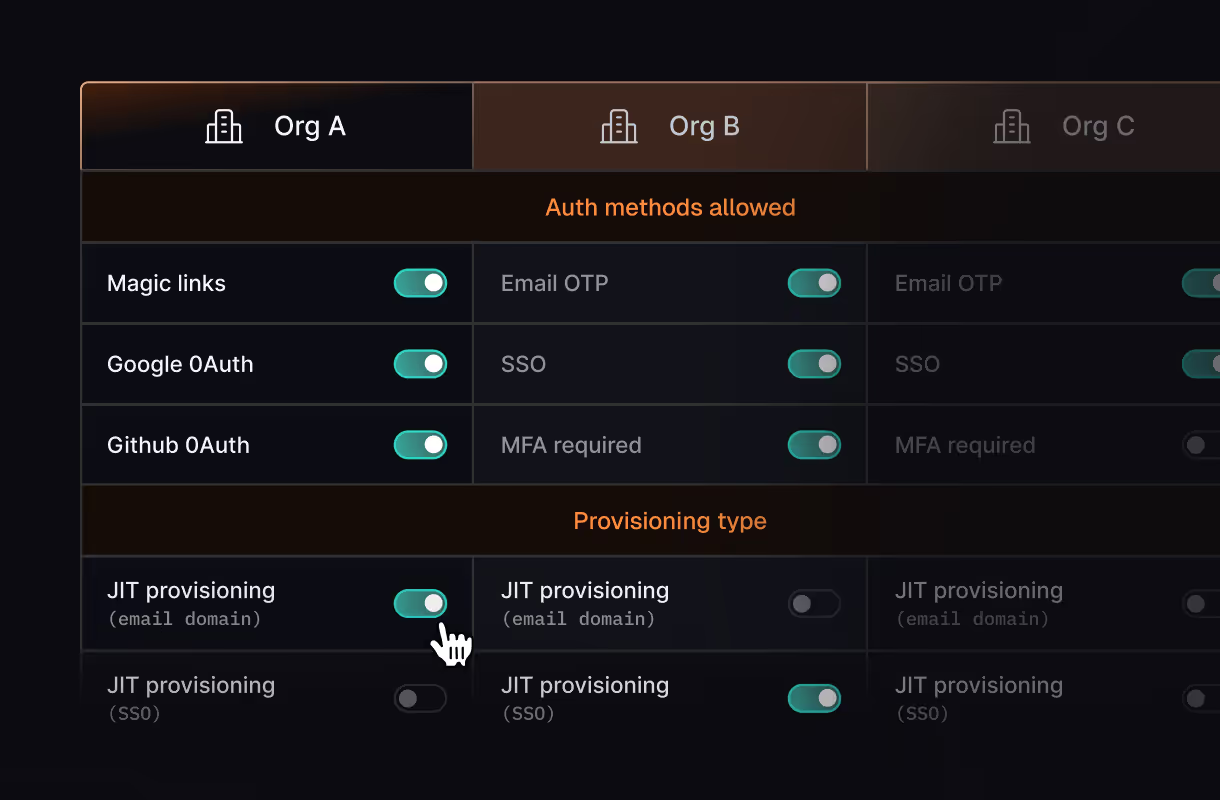
Organization-scoped access
Roles, permissions, and access checks are evaluated within organization context — not reassembled in application code
Memberships and users, modeled for B2B
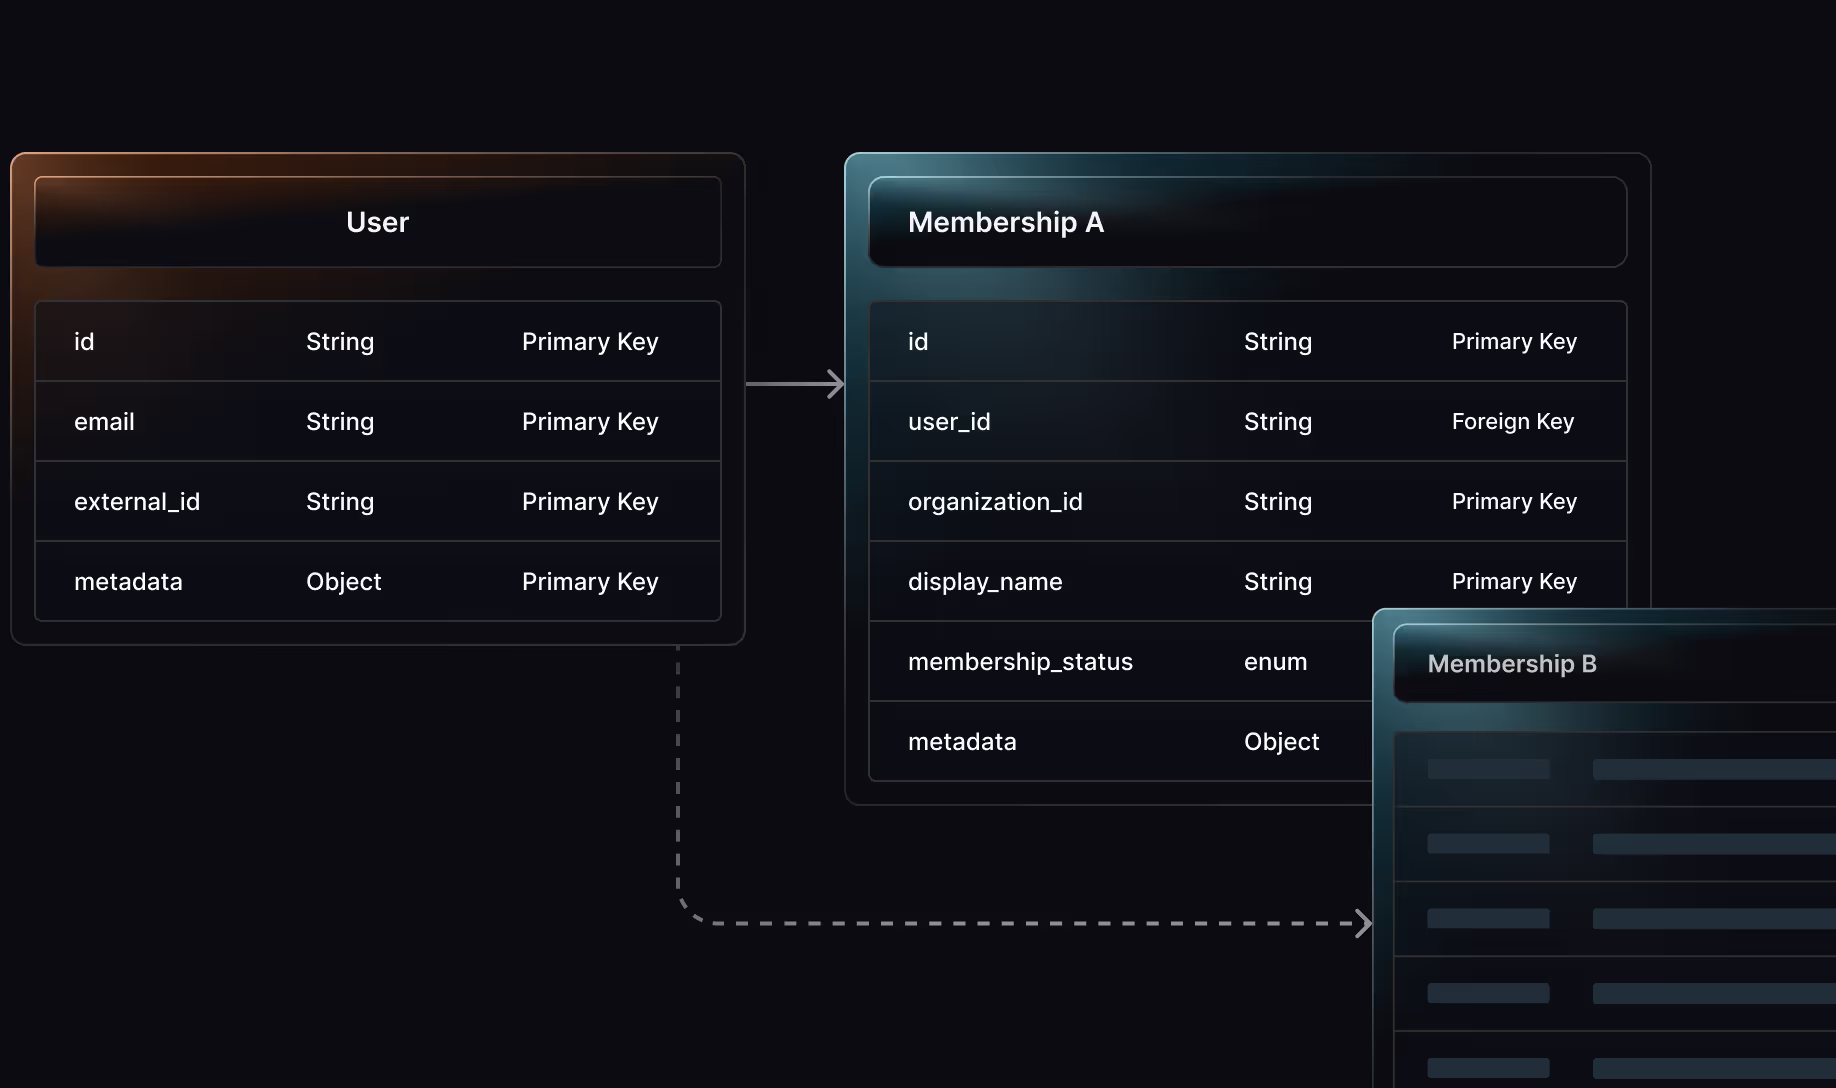
Memberships define a user's relationship to an organization, including roles, status, and access context
View docs
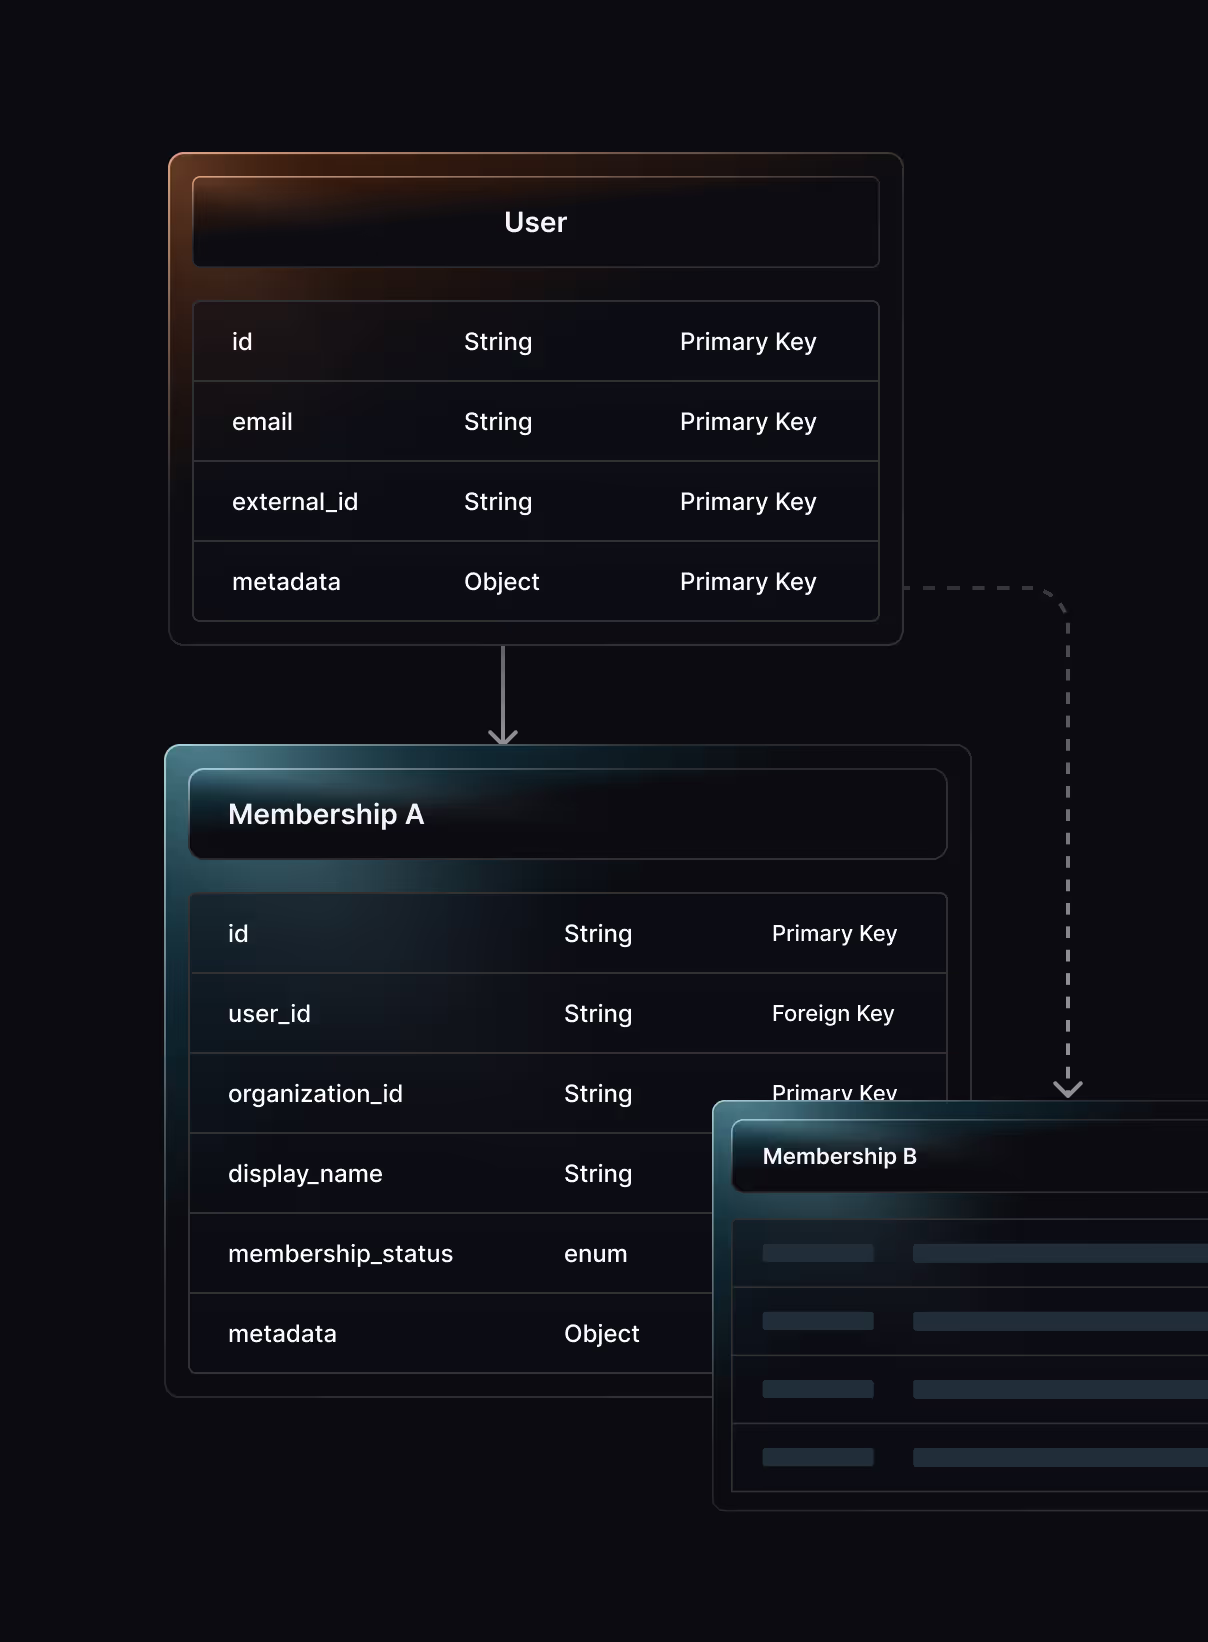
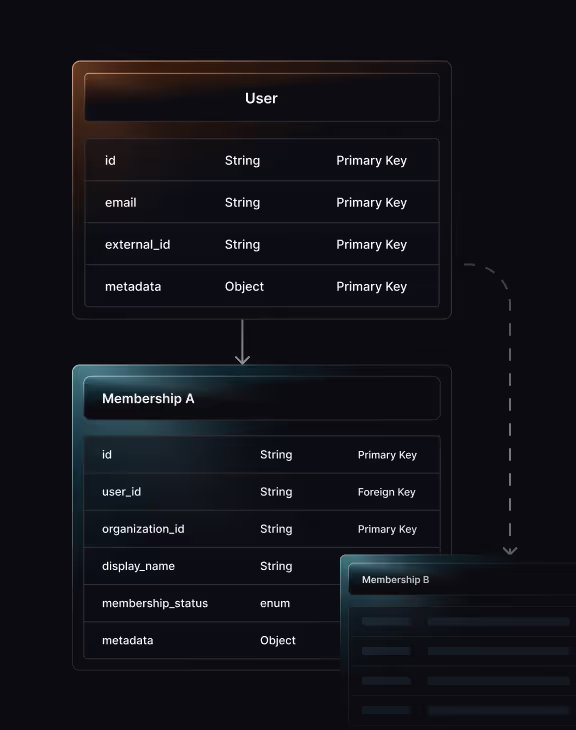
Membership defines user–organization relationships
Memberships link users to organizations and carry roles, status, and access context
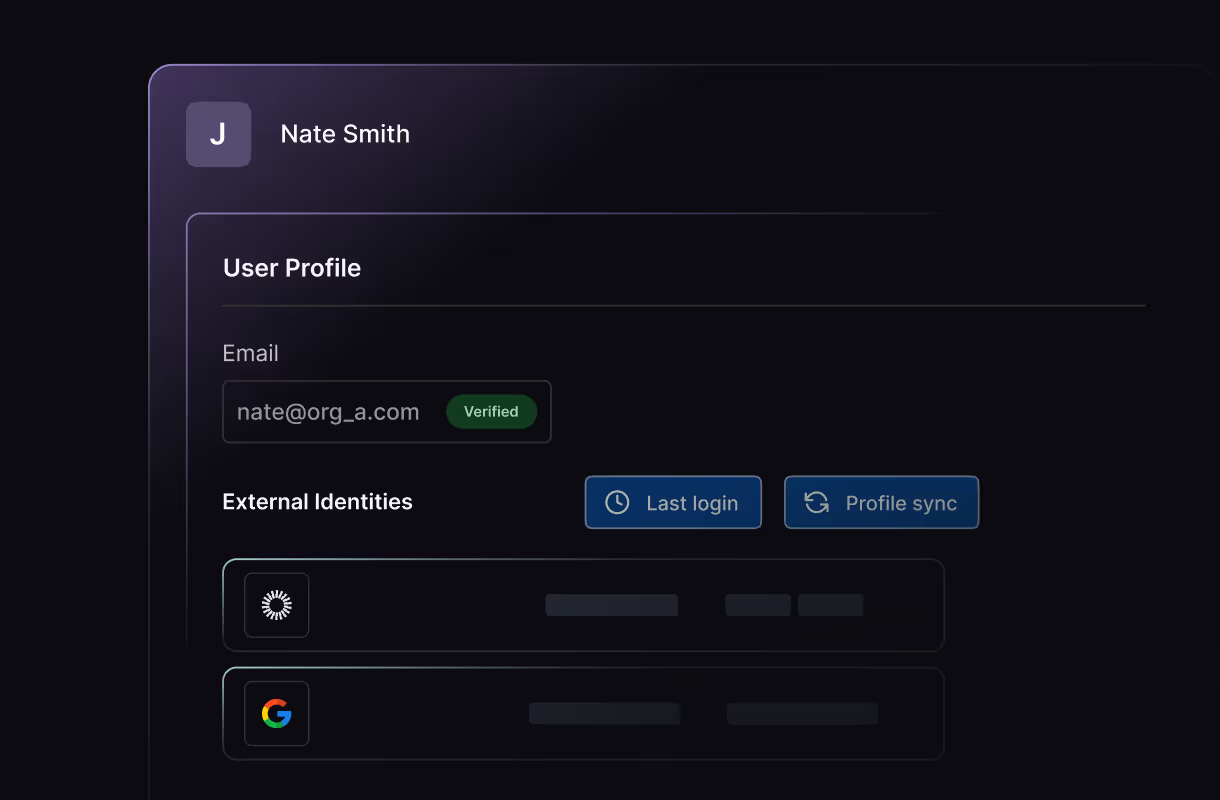
User identity de-duplication
Users signing in through different auth methods are resolved to a single identity - no duplicate user records
Shared users across organizations
A single user can belong to multiple organizations through separate memberships — no duplicate accounts, no custom coding
Built-in provisioning flows, without identity fragmentation
Support signup, user invites, and enterprise onboarding flows — while preserving a clean user and organization model underneath
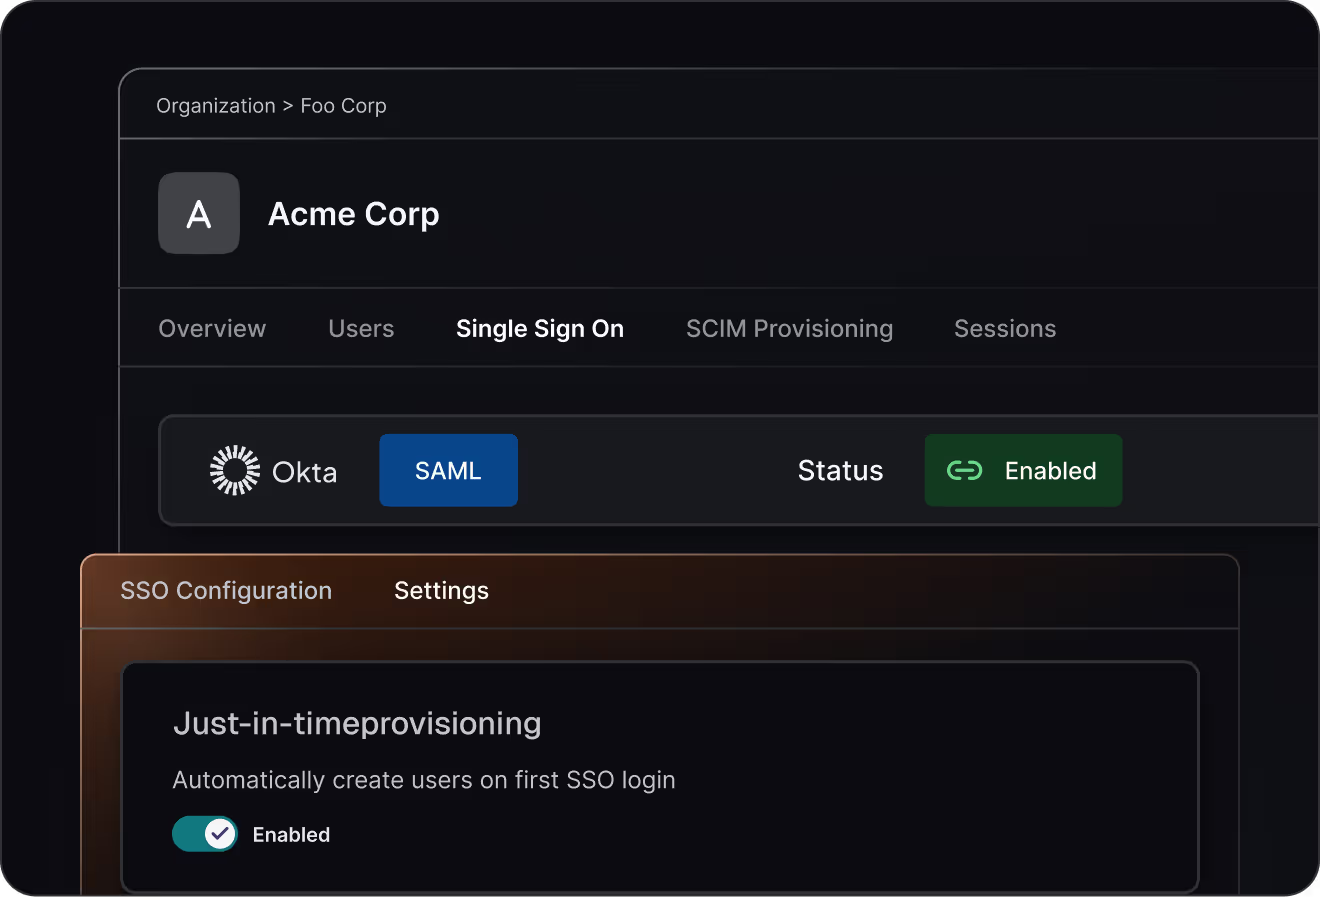
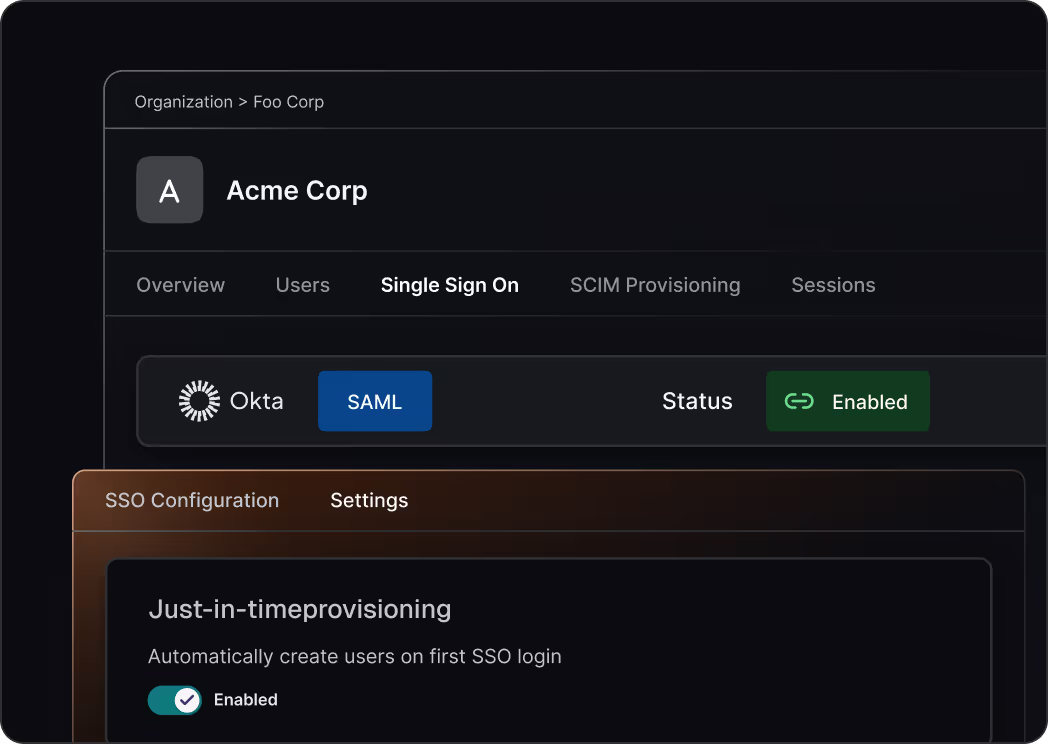
Just-in-time user provisioning
Automatically create users in the correct organization on first SSO login
No pre-provisioning, manual invites, or admin overhead required
Read docs
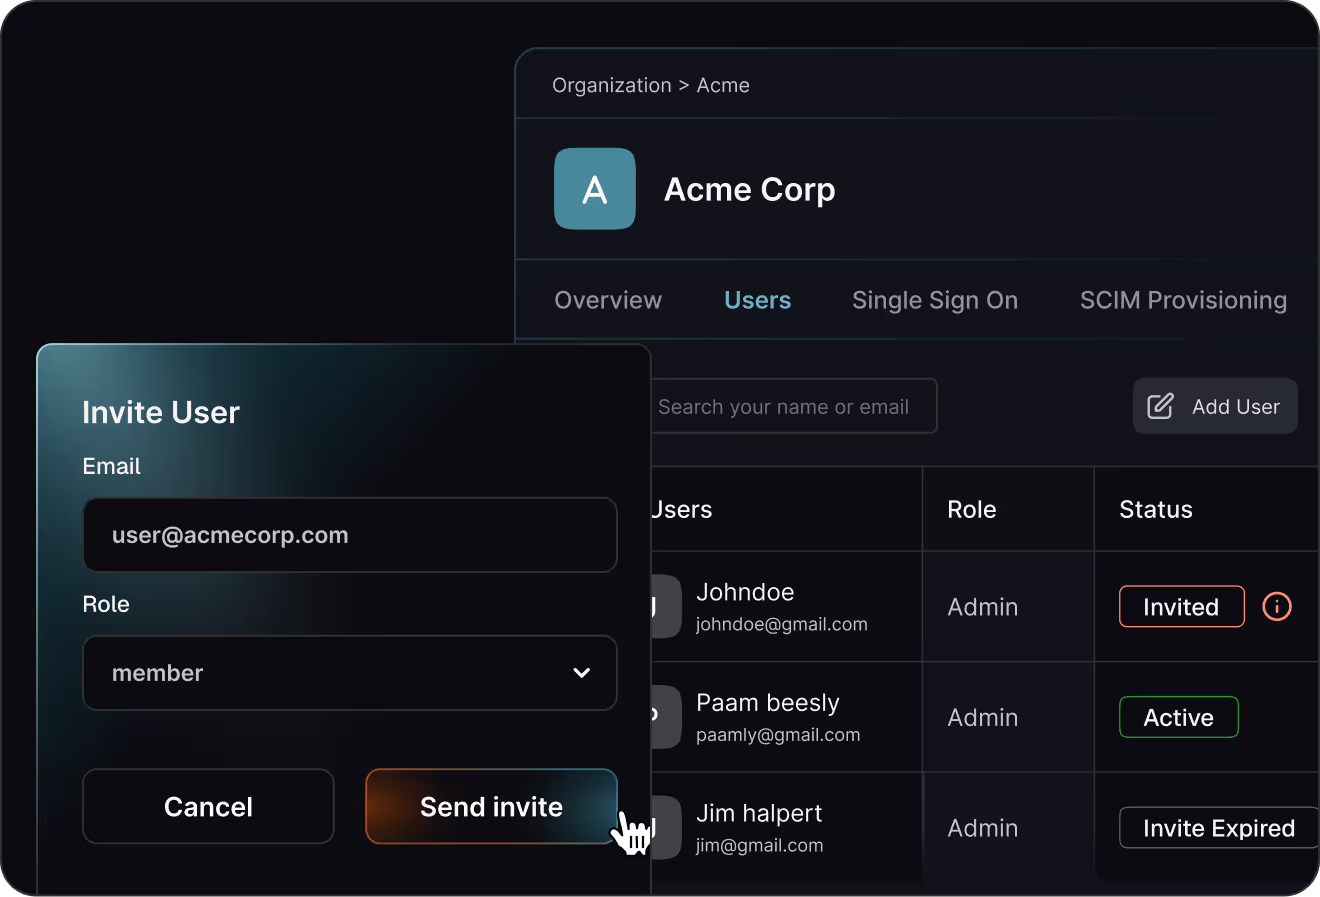
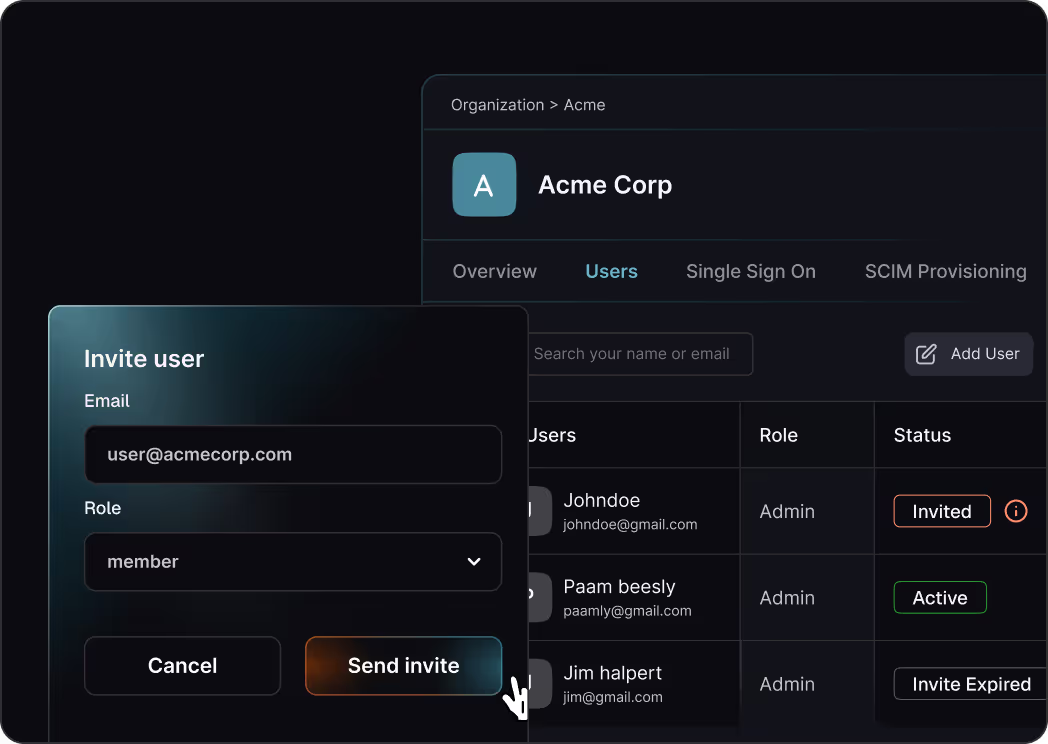
Invite users to organizations
Invite users to specific organizations directly from your app
Assign roles upfront, so access is predictable from day one
Read docs
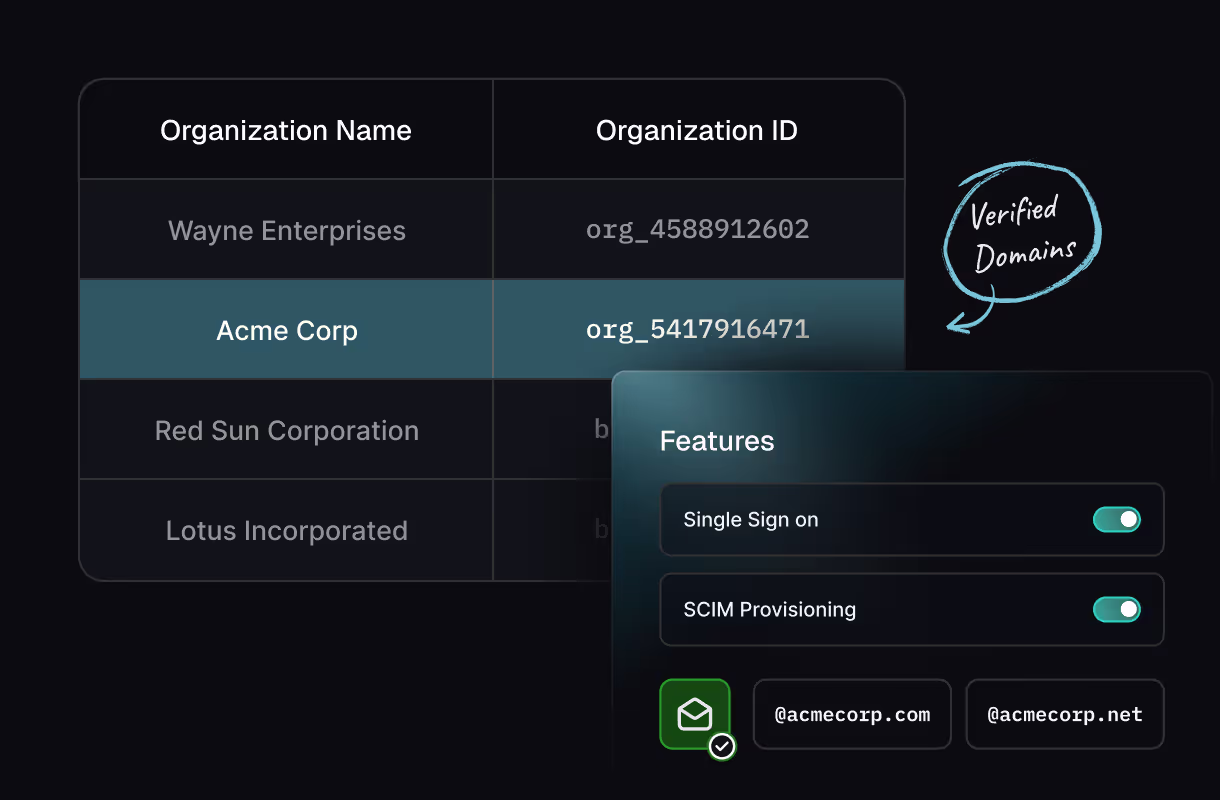
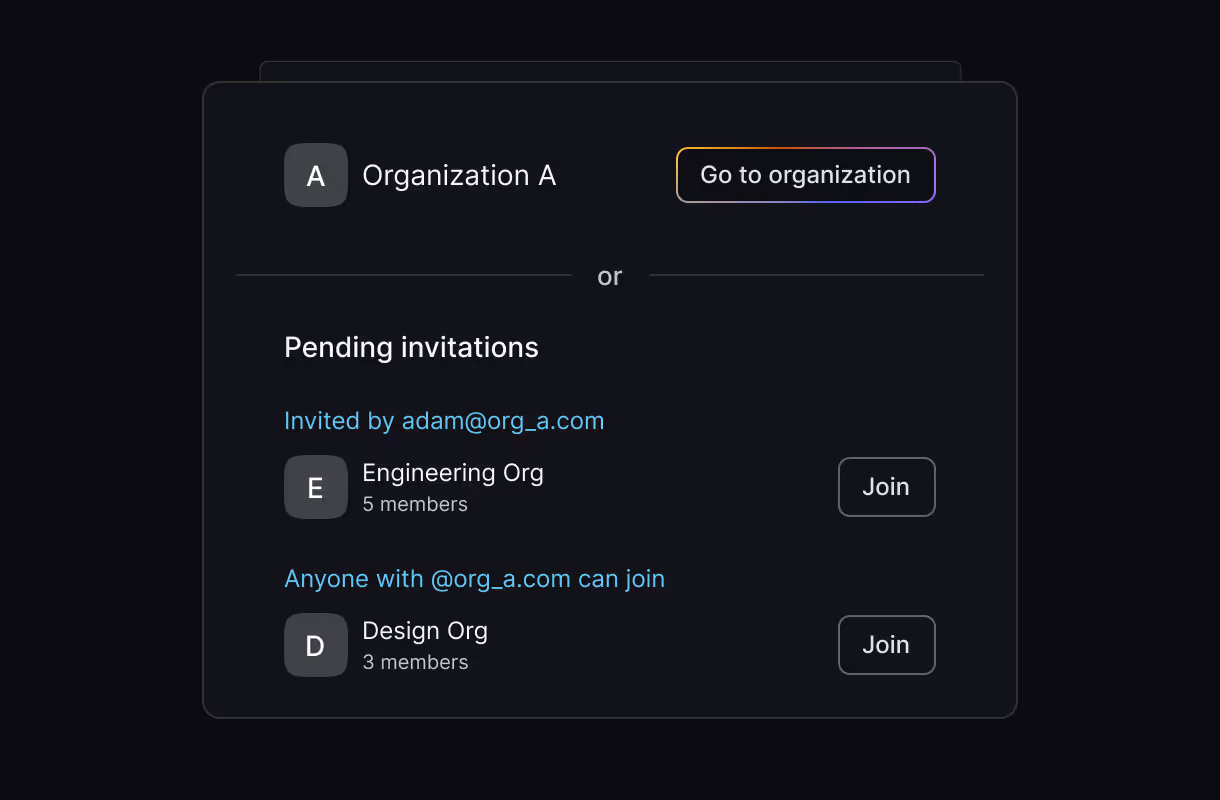
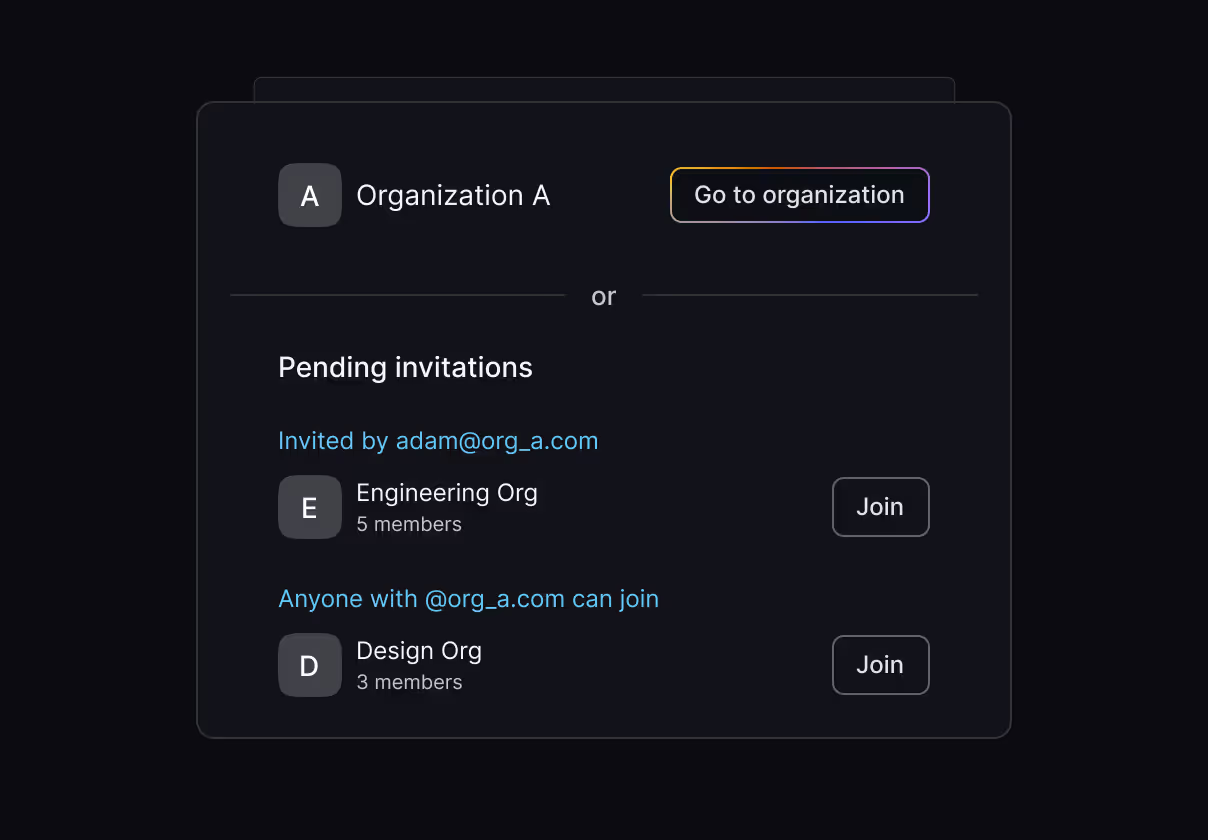
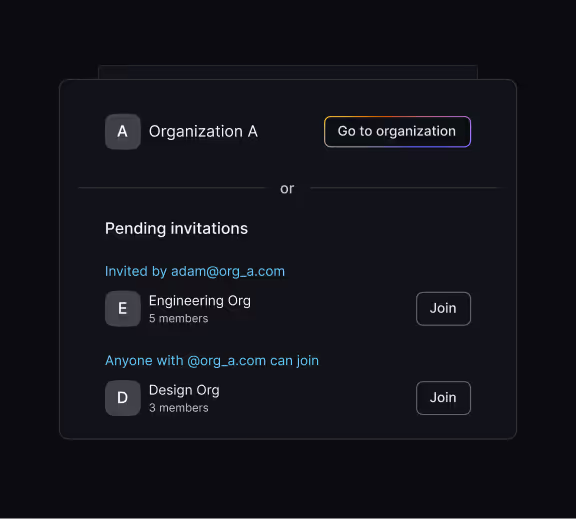
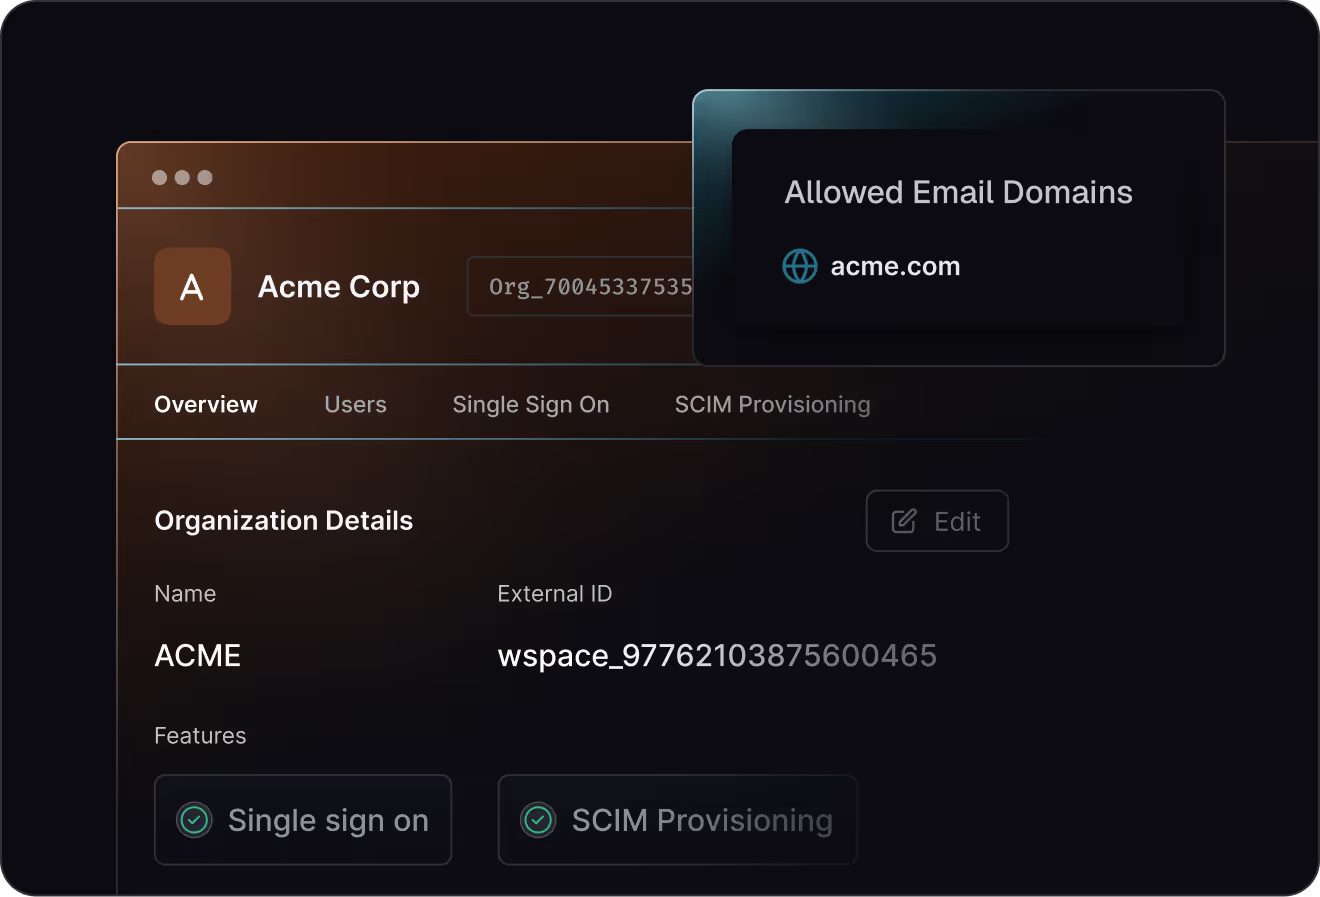
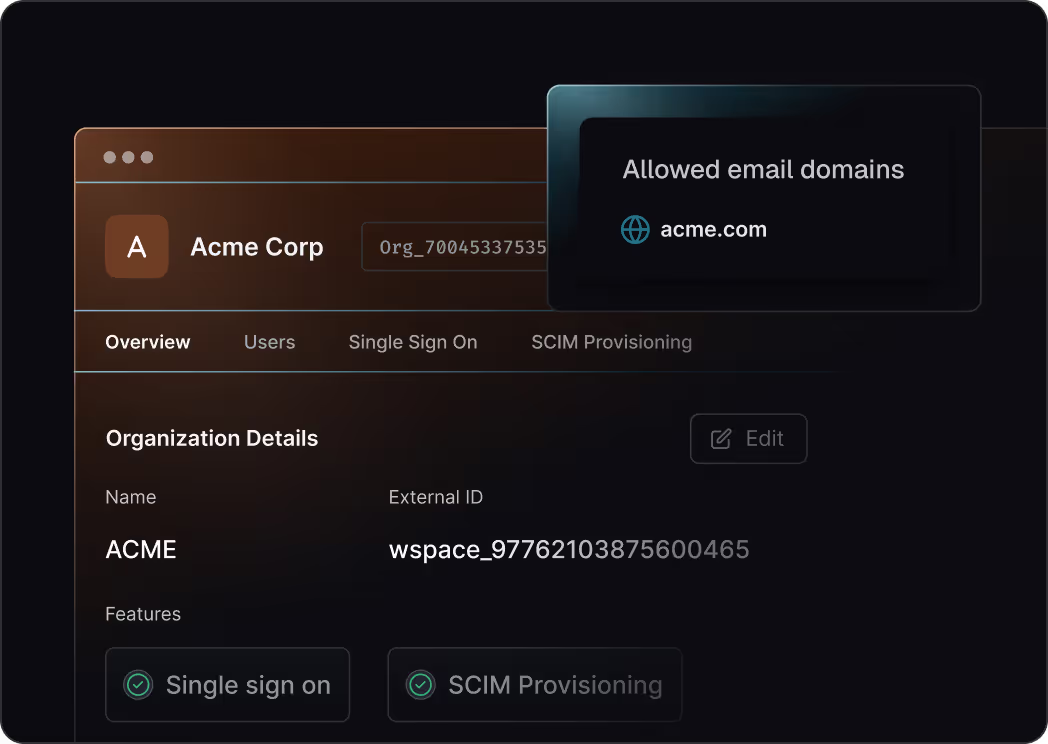
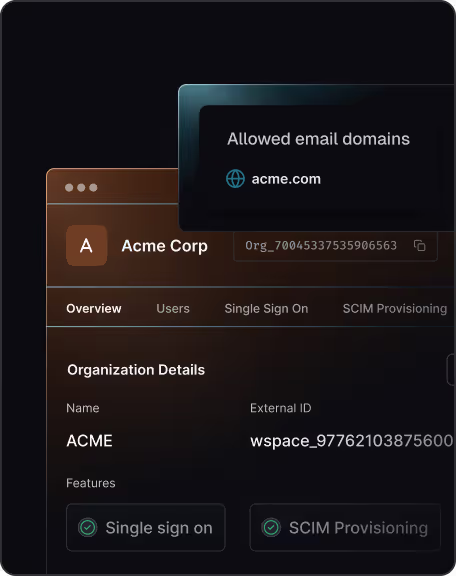
Route users by allowed email domains
Automatically route users to the right organization during signup
Prevent duplicate orgs and accidental misrouting
Read docs
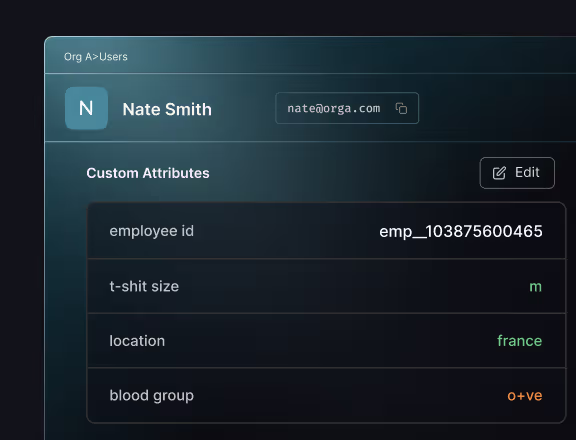
Extend users and organizations with business context
Attach business context to users and organizations — without brittle workarounds in your app code
Read docs
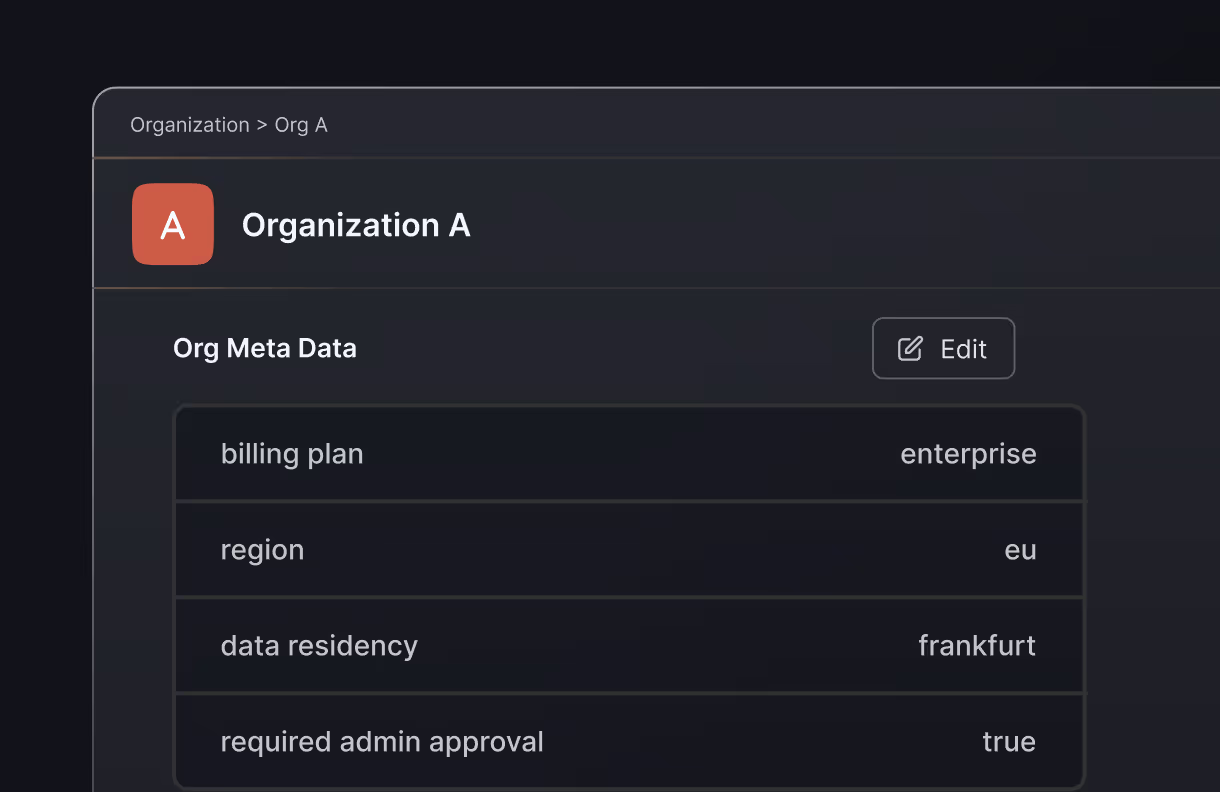
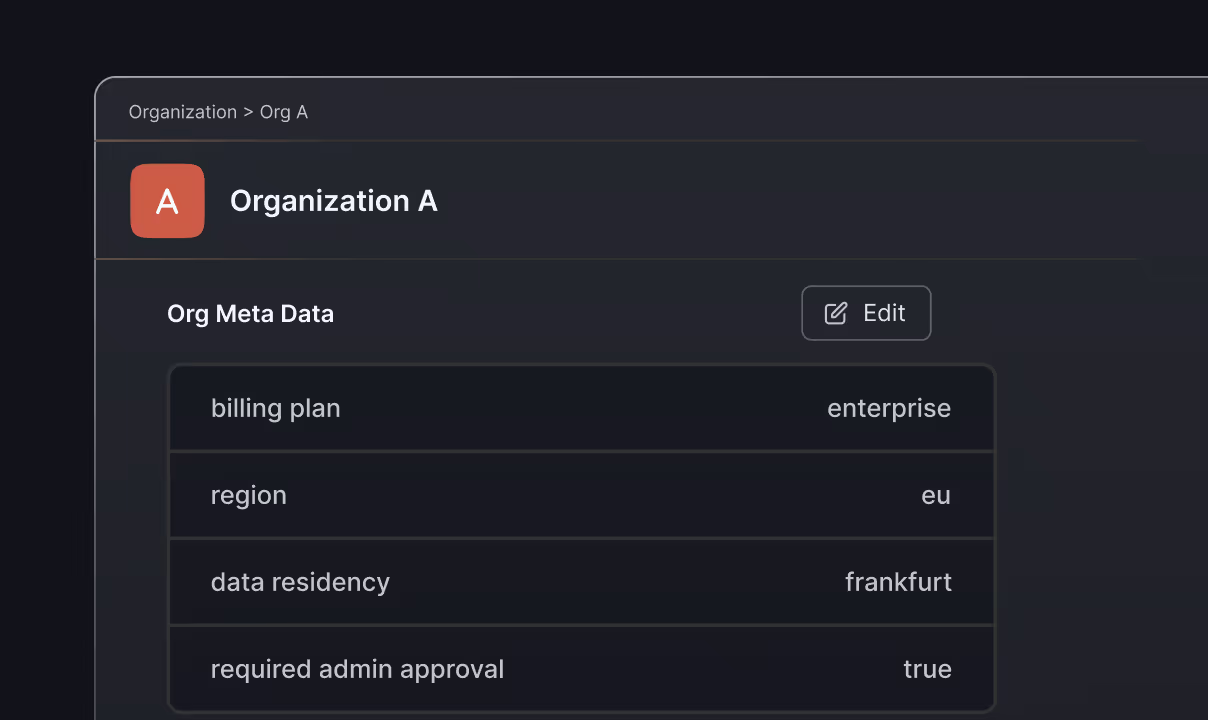
Add organization metadata
Add billing plans, regions, and compliance flags to organizations — and use them directly in access control, routing, and policy decisions
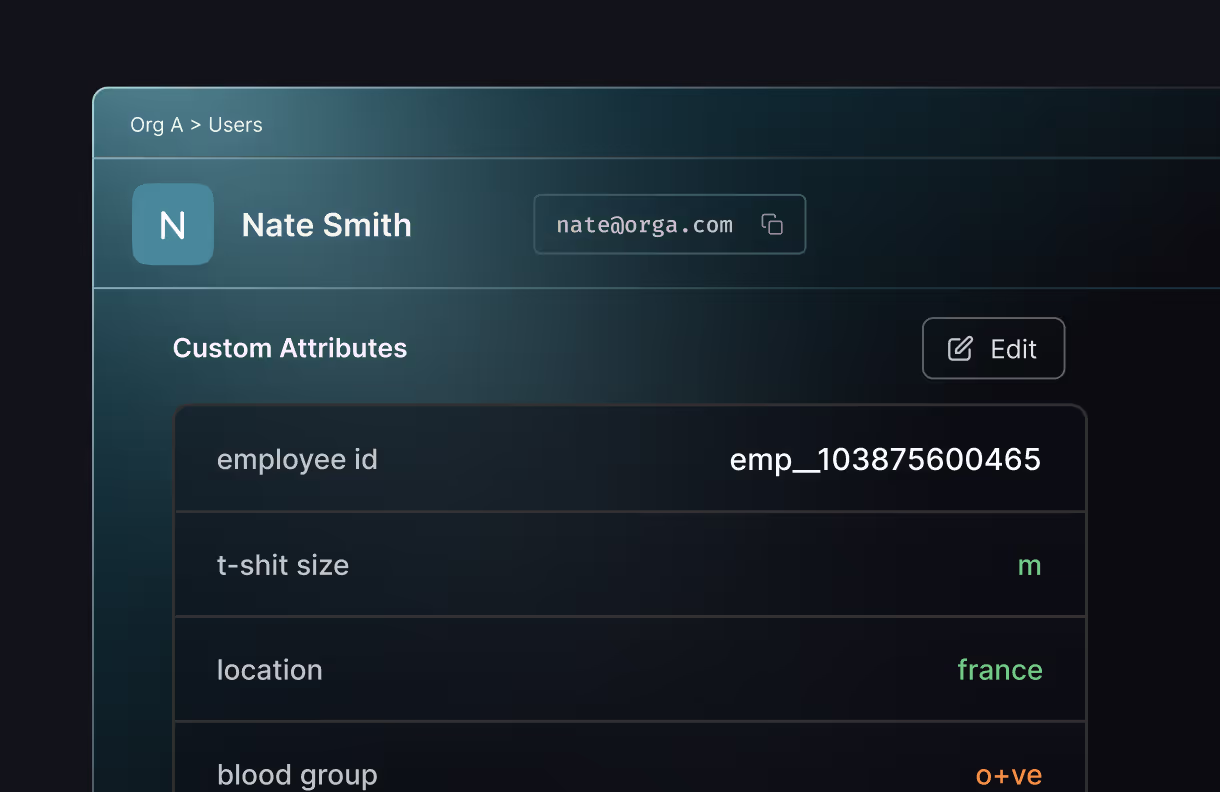
Extend user identity without schema changes
User-level metadata helps you store internal user IDs, external references, and evolving user attributes
Scope authorization to the organization
Access is evaluated against the active org and membership, so roles and permissions stay consistent as users switch contexts
View docs
We use cookies, so things load fast, we learn what to fix, and you can always reach us on chat
Okay, got it!