

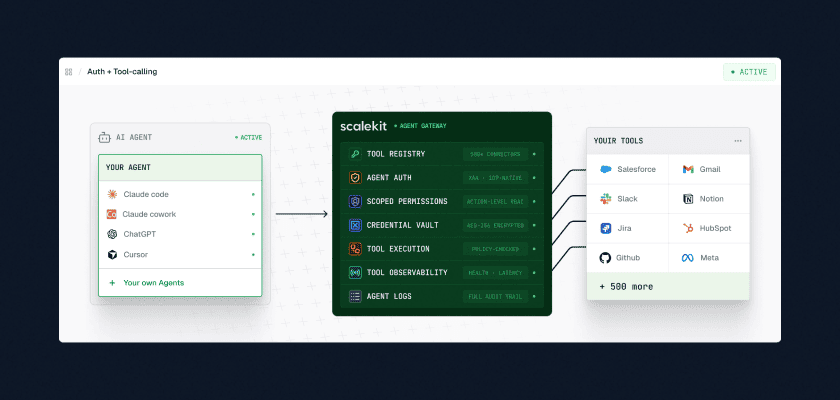
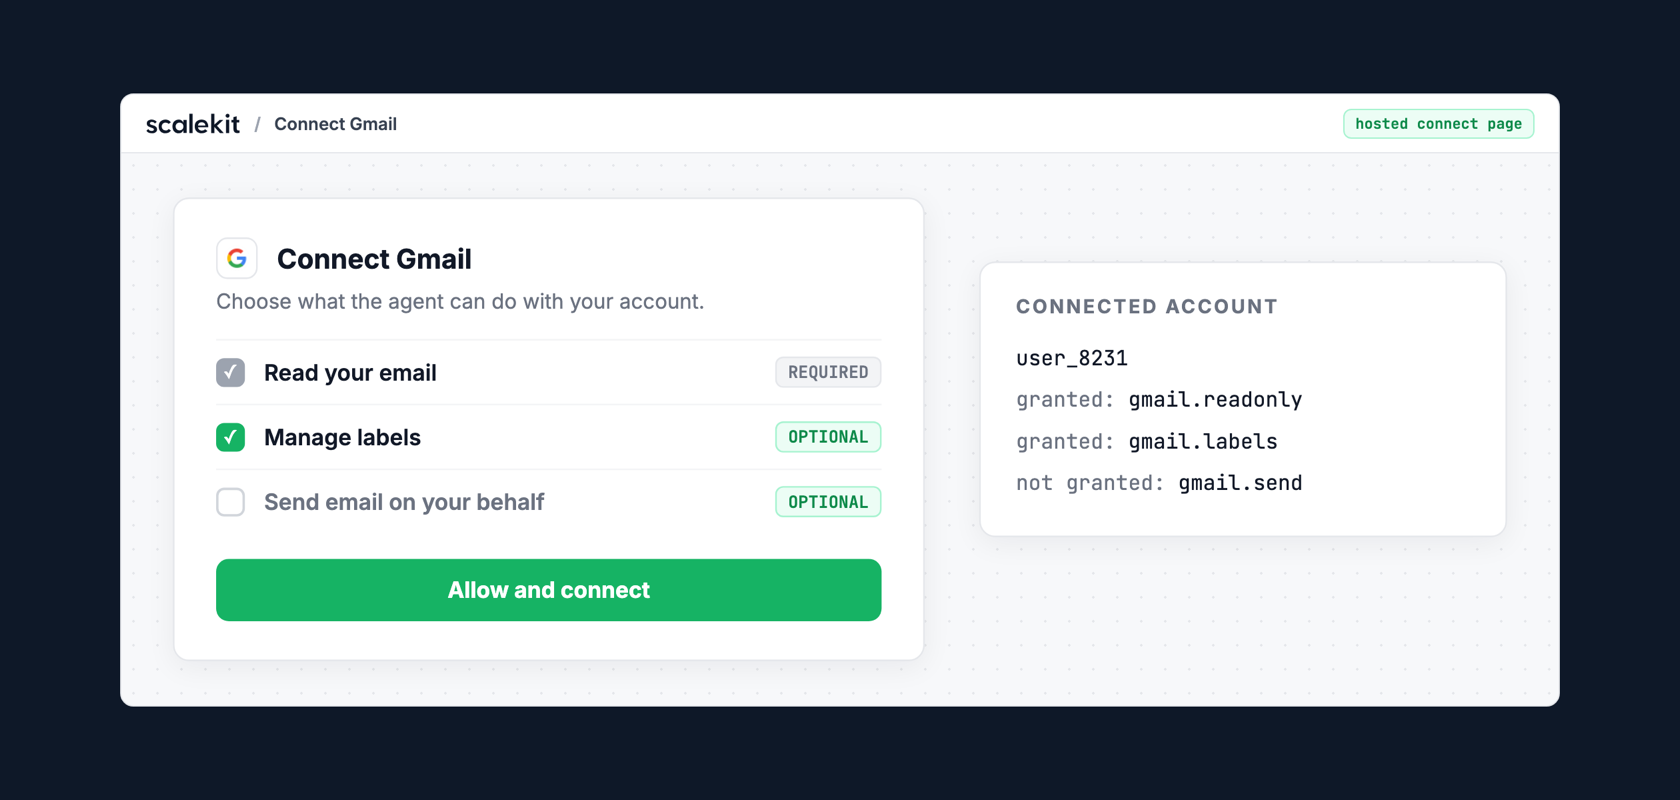
Some apps belong to the team rather than to one person: the company HubSpot account, a shared support inbox, an internal API with one key. Until now, every user had to connect their own account before an agent could act in an app for them, even when they had no seat in it.
With org-wide credentials, an admin connects the app once with a shared OAuth or API key credential, and everyone in the organization can use it through their agents. Identity stays per user: each tool call made through the shared credential is logged under the user who made it, and admins still decide which tools each user can reach.
Take a prospecting agent built on a company-wide Apollo API key. An admin creates an org-wide connection with that key. Every rep's agent can search and enrich contacts through it without each rep holding an Apollo login, and the audit log shows which rep ran each search.
How it works
- Choose org-wide mode when you create the connection and enter the credential once. The mode is set at creation, so to move an existing connection to org-wide, create a new one.
- The shared credential is stored as one connected account with is_org_wide_credential set to true, and you can filter on that field when listing connected accounts.
- Every tool call through the shared credential is attributed to the calling user.
- Admins can delete an org-wide credential from the dashboard.
Read the connected accounts API reference.


